Addressing Cybersecurity Risks: New Checklist for CPAs in the Age of AI
With AI heightening cybersecurity threats, a new checklist provides CPAs a structured approach to safeguarding their firms against emerging risks.
The cybersecurity landscape has transformed into an intense battlefield, particularly as the integration of artificial intelligence (AI) technologies escalates the risks for organizations, especially in finance and accounting sectors. With attackers employing AI tools that enable them to execute sophisticated deceptions and identify vulnerabilities at a rapid pace, the urgency for finance professionals to reassess their cybersecurity strategies has never been clearer.
According to Sanjay Chadha, CPA/CITP, and founding partner at SAV Associates, “The threat environment is becoming significantly more serious. It has become much more dangerous, and the speed at which the threat landscape is changing has accelerated significantly.” This growing threat is particularly worrisome given the vast amounts of sensitive data handled by finance departments and accounting firms.
Foundation of Security: The Baseline Checklist
To tackle these challenges, Chadha has developed a “Baseline Security Checklist,” a practical tool designed to help professionals gauge their cybersecurity maturity. This checklist merges fundamental elements from several existing cybersecurity standards into a cohesive framework, enabling organizations to assess their security posture against criteria that reflect evolving risks.
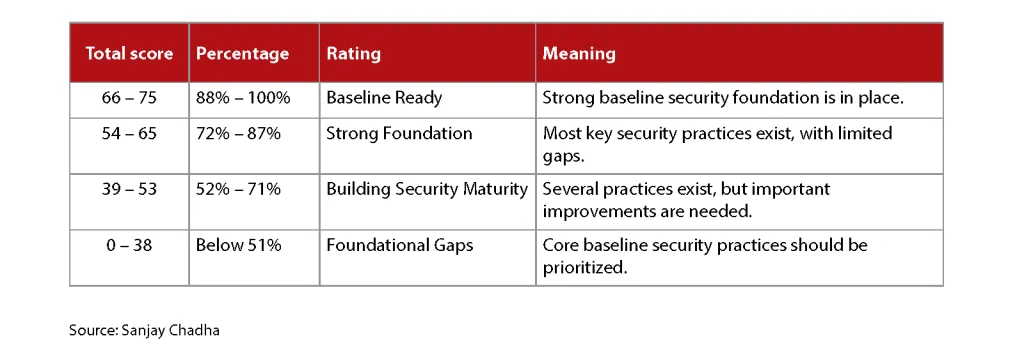
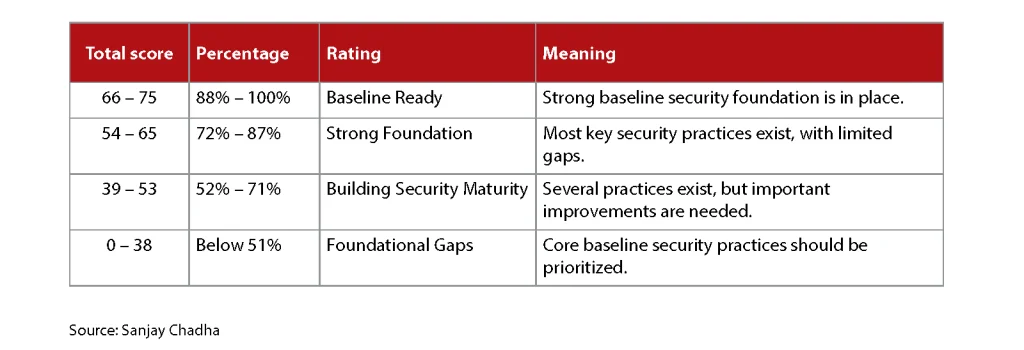
The checklist includes twelve core security areas, with checkpoints designed to score practitioners on a scale of up to 75 points. As outlined in the introduction, “The problem isn’t choosing the ‘right’ framework. It’s knowing whether you’ve covered the fundamentals.” Each area, from resilience and recovery to AI governance, demands attention to ensure that firms are not caught off guard by emerging threats.
Navigating AI Risks
AI's rapid integration into business processes brings profound implications for data privacy and security. Chadha’s checklist emphasizes the necessity for organizations to define acceptable AI use, restrict unauthorized data flow into AI tools, and conduct thorough reviews of AI-generated outputs prior to operational deployment.
Establishing a framework for authorized AI tools is imperative. Firms should consider utilizing enterprise-level solutions, such as OpenAI's ChatGPT or Anthropic's Claude, which may offer enhanced security measures. However, the risk associated with AI doesn’t stop here. Individuals in positions of less technical expertise can utilize AI to write code, a practice referred to as "vibe coding," which invites significant risk into the security landscape.
Steven Ursillo, CPA/CITP, CGMA, highlights that as user-driven development expands, it’s critical to implement a review process for AI-generated applications to safeguard against potential vulnerabilities. Inadequate tracking of AI-generated innovations may create challenges in managing workflows and maintaining security, hence the importance of clear governance protocols cannot be overstated.
Establishing Governance and Data Classification
Governance over AI tools and data usage is critical in the new landscape. The checklist indicates that it is the responsibility of finance departments to comprehend where and why AI applications are being used. While experimentation with AI capabilities is essential for growth, governance is necessary to prevent unauthorized access and ensure compliance with data protection standards.
Paul Perry, CPA/CITP, emphasizes that effective governance is about fostering an environment where employees understand their boundaries rather than imposing excessive controls that can lead to workarounds. Implementing a data classification policy that ranks information based on sensitivity and risk can further enhance security measures.
The checklist also advocates establishing protocols to prepare for potential security incidents. Organizations need to have robust incident response plans that outline the immediate steps to be taken in the event of a data breach, including the importance of backing up data and having business continuity plans in place.
Furthermore, finance departments must maintain a close eye on third-party risks, as partnerships with vendors can introduce new vulnerabilities into their security frameworks. Regular assessments and assurance reviews can help mitigate these risks and maintain a secure operational environment.
Fundamental Defenses Against Evolving Threats
The risks posed by AI aren’t limited to those actively using these technologies; organizations without AI capabilities are still under threat as attackers leverage AI to conduct social engineering and cyberattacks. The speed of potential breaches will likely accelerate as exploitations become more sophisticated.
Chadha points out that breaches can now happen much more rapidly, necessitating immediate responses from finance departments. He references instances where AI has been utilized to conduct cyberattacks, underscoring the pressing need for organizations to maintain current software, regularly apply necessary patches, and proactively identify vulnerabilities in their systems.
Organizations can reinforce their defenses through various foundational cyber techniques, including:
- Implementing role-based access control to limit data access to necessary users only.
- Logging user actions, which can help identify compromised accounts.
- Employing multifactor authentication to bolster login security.
- Utilizing dual authorization for significant transactions to combat potential AI-driven fraud.
Fostering a Culture of Continuous Improvement
While many organizations struggle to implement essential defenses, Chadha encourages a measured approach to remedying cybersecurity practices. He promotes the idea of “defense in depth,” where layered defenses fortify security, allowing firms to gradually improve their cybersecurity posture without succumbing to panic.
"It’s not a panic game where everything has to be implemented in one go," he asserts. "Everything has cost. Try to adopt a step-by-step process." This strategy emphasizes starting with a clear understanding of an organization’s existing systems and data, followed by prioritizing defense implementations based on risk assessments.
Perry adds that building a secure environment involves evolving organizational culture, enhancing governance, comprehensive training, and investing in tailored software improvements. Firms do not need to achieve a perfect security program immediately; rather, they should aim for foundational stability and keep enhancing over time.
Utilizing the Checklist for Enhanced Security
Chadha’s checklist, which integrates core cybersecurity requirements from widely recognized frameworks, serves as a useful starting point for practitioners eager to improve their cybersecurity readiness. The approach involves evaluating a range of fundamental security aspects across twelve designated areas that align with prevalent standards such as NIST CSF, CIS Controls, and ISO 27001.
To utilize the checklist effectively, firms should conduct an honest self-assessment, checking off measures that have been implemented rather than idealized plans. Each completed item contributes to an overall score, allowing organizations to benchmark their practices against established grading categories, from “Baseline Ready” for high scorers to identification of urgent foundational gaps for lower scoring firms.
Next Steps and Long-Term Strategy
Once organizations identify their weaknesses via the checklist, they should prioritize two to three areas that represent the highest risk and assign responsibility for improvements accordingly. A periodic reassessment every few months can help track progress and recalibrate focus as necessary.
Cybersecurity threats are ever-changing and remain a daunting challenge for finance and accounting professionals. However, utilizing straightforward tools like Chadha’s checklist can facilitate a structured approach to evolving defensive measures, ensuring that organizations remain one step ahead of potential attackers. As cybersecurity continues to be a pressing concern, embracing proactive measures through ongoing learning and adaptation will be essential to safeguarding sensitive information.
In summary, while evolving AI technologies present new vulnerabilities, structured governance, a solid security foundation, and continuous improvement initiatives will enable finance professionals to build resilience against cyber threats effectively.
Organizations must remember: adopting the checklist is just one step in a continuously evolving cybersecurity landscape. There are no foolproof solutions, but consistent efforts and a culture of responsibility can significantly reduce risks associated with cybersecurity in the age of AI.